-20%

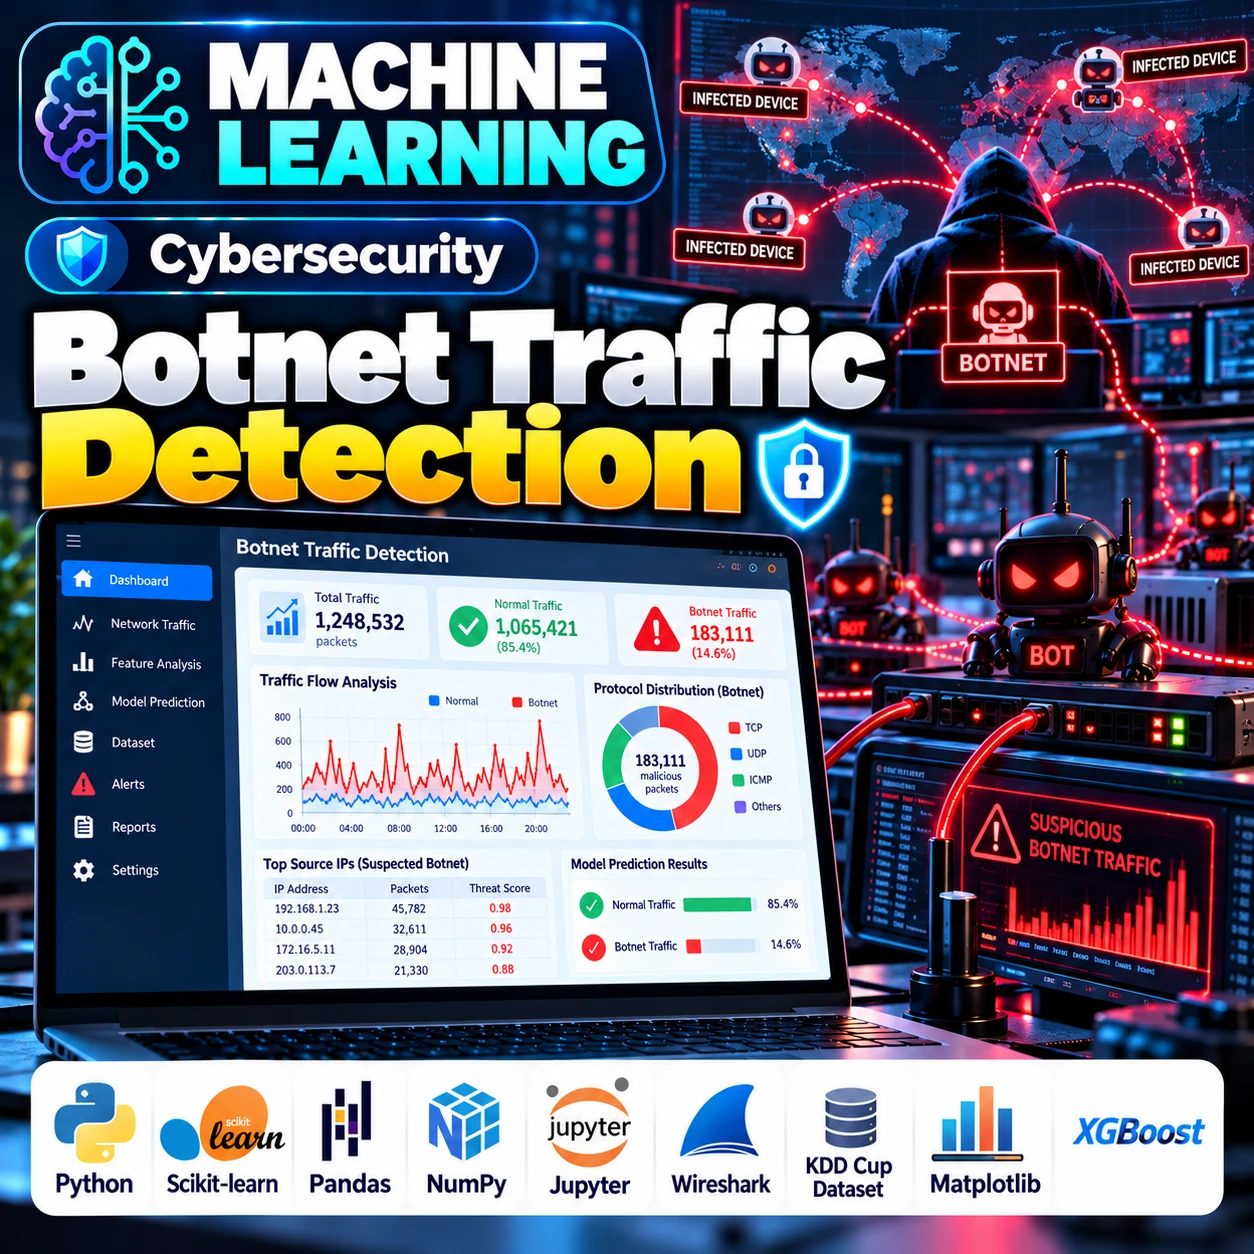
Botnet Traffic Detection

0 Orders 0 Wish listed

₹4,999.00

Qty
Total price:
  ₹4,999.00

Detail Description

1. Abstract

Botnet Traffic Detection is a cybersecurity and machine learning project designed to identify network traffic generated by compromised devices that may be controlled as part of a botnet. Botnets can be used for activities such as distributed denial-of-service (DDoS) attacks, spam distribution, automated scanning, credential attacks, and other malicious operations.

The system analyzes network traffic and connection-level features such as packet counts, byte volume, connection duration, protocol, source and destination information, connection frequency, port activity, and traffic patterns. Machine learning algorithms are used to distinguish normal network traffic from potentially malicious botnet-related traffic and provide security alerts for further investigation.

2. Objectives

  1. Detect potentially malicious botnet traffic automatically.
  2. Classify network traffic as normal or suspicious.
  3. Identify abnormal communication patterns.
  4. Analyze network connections and traffic behavior.
  5. Detect repeated or unusual communication activities.
  6. Reduce manual network monitoring effort.
  7. Apply machine learning to network security.
  8. Generate alerts for suspicious traffic.
  9. Support early identification of compromised devices.
  10. Provide a visual network-security monitoring dashboard.

3. Existing System

Traditional botnet detection methods commonly use:

  1. Signature-based intrusion detection.
  2. Firewall rules.
  3. IP and domain blacklists.
  4. DNS monitoring.
  5. Manual network monitoring.
  6. Known malware signatures.
  7. Static traffic rules.
  8. Security Information and Event Management (SIEM) systems.

Limitations

  1. Known signatures may not detect new botnet variants.
  2. Blacklists require continuous updates.
  3. Sophisticated botnets can modify their communication patterns.
  4. Large volumes of network traffic are difficult to monitor manually.
  5. Static rules may generate false positives.
  6. Encrypted or changing communication patterns can make detection difficult.
  7. Previously unseen botnet behavior may not match existing signatures.

4. Proposed System

The proposed system uses machine learning and network traffic analysis to identify potentially botnet-related communication.

The system can analyze features such as:

  1. Source and destination IP information
  2. Source and destination ports
  3. Network protocol
  4. Connection duration
  5. Number of packets
  6. Bytes sent and received
  7. Packet size statistics
  8. Connection frequency
  9. Flow duration
  10. TCP flags
  11. Failed connections
  12. Port activity
  13. Incoming/outgoing traffic ratio
  14. Repeated connection patterns
  15. DNS-related features, when available

Possible algorithms include:

  1. Logistic Regression
  2. Decision Tree
  3. Random Forest
  4. Support Vector Machine (SVM)
  5. K-Nearest Neighbors (KNN)
  6. Gradient Boosting
  7. XGBoost
  8. Isolation Forest for anomaly detection

The system can classify traffic into categories such as:

Normal Traffic → Low Risk

Suspicious Traffic → Requires Investigation

Botnet/Attack Traffic → High Risk

The exact classes depend on the dataset and project implementation.

5. Implementation Procedure

Step 1: Data Collection

Collect network-flow or connection-level datasets containing normal and malicious traffic.

Possible datasets include publicly available cybersecurity datasets such as CICIDS2017, UNSW-NB15, or other suitable network-security datasets.

Step 2: Data Preprocessing

  1. Remove duplicate records.
  2. Handle missing values.
  3. Clean inconsistent network records.
  4. Encode categorical variables.
  5. Normalize numerical features where required.
  6. Handle class imbalance when necessary.

Step 3: Network Feature Extraction

Extract relevant traffic characteristics such as:

  1. Flow duration
  2. Packet count
  3. Byte count
  4. Packet size
  5. Protocol
  6. Port information
  7. Connection frequency
  8. TCP flags
  9. Source/destination behavior
  10. Traffic direction

Step 4: Exploratory Data Analysis

Analyze:

  1. Normal vs malicious traffic distribution
  2. Protocol usage
  3. Port activity
  4. Packet patterns
  5. Connection frequency
  6. Traffic volume
  7. Suspicious communication patterns

Step 5: Feature Selection

Select the most useful network features to improve model performance and reduce unnecessary data.

Step 6: Model Training

Split the dataset into training and testing sets and train multiple machine learning models.

Step 7: Model Evaluation

Evaluate the models using:

  1. Accuracy
  2. Precision
  3. Recall
  4. F1-Score
  5. ROC-AUC
  6. Confusion Matrix

For botnet detection, recall is particularly important because failing to detect malicious traffic can allow compromised systems to remain active.

Step 8: Traffic Prediction

New network-flow records are processed by the trained model and classified according to their learned traffic patterns.

Step 9: Security Dashboard

Develop a Streamlit or Flask-based dashboard displaying:

  1. Network traffic statistics
  2. Source/destination information
  3. Protocol distribution
  4. Traffic volume
  5. Suspicious connections
  6. Botnet detection result
  7. Risk level
  8. Detection history
  9. Traffic visualization
  10. Security alerts

6. Software Requirements

  1. Operating System: Windows / Linux
  2. Programming Language: Python
  3. IDE: VS Code / Jupyter Notebook / Google Colab
  4. Libraries: Pandas, NumPy, Scikit-learn
  5. Visualization: Matplotlib / Seaborn / Plotly
  6. Web Framework: Streamlit or Flask
  7. Network Analysis: Scapy / PyShark (optional, depending on implementation)
  8. Database: SQLite / MySQL (optional)
  9. Browser: Google Chrome / Microsoft Edge
  10. Dataset: Network traffic/botnet detection dataset

7. Hardware Requirements

  1. Processor: Intel Core i3 or equivalent
  2. RAM: Minimum 4 GB
  3. Storage: Minimum 10 GB free space
  4. Display: 1366 × 768 or higher
  5. Keyboard and Mouse: Standard
  6. Internet: Required for dataset and software installation
  7. GPU: Not required for traditional machine learning models

8. Advantages of the Project

  1. Automated botnet traffic detection.
  2. Identifies suspicious network communication patterns.
  3. Helps detect potentially compromised devices.
  4. Reduces manual network monitoring.
  5. Supports machine learning-based cybersecurity.
  6. Can analyze large network traffic datasets.
  7. Helps identify abnormal communication behavior.
  8. Provides visual traffic analysis.
  9. Generates security alerts for suspicious connections.
  10. Can be extended for real-time network monitoring.
  11. Supports multiple machine learning algorithms.
  12. Can be integrated with broader intrusion-detection systems.


No review given yet!

Fast Delivery all across the country
Safe Payment
7 Days Return Policy
100% Authentic Products

You may also like

View all

AI Lesson-Plan Generator

₹4,999.00

AI Question-Paper Generator

₹4,999.00

AI Resume Builder

₹4,999.00

College Knowledge-Base Chatbot

₹4,999.00

Data Lake-Based Healthcare Analytics

₹4,999.00

Botnet Traffic Detection
₹4,999.00 ₹0.00
₹4,999.00
4999